
How to Hire for Cyber Incident Response Before a Crisis
Hiring for cyber incident response before a crisis means recruiting someone who can make sound decisions under pressure, not simply someone who knows security tools. For a CEO, COO or talent leader, the challenge is defining the authority, technical depth and operational cover the business needs before an incident exposes the gaps.
Start with the consequences you need to manage: interrupted revenue, compromised customer data, unavailable services or disrupted production. Then build the role, assessment process and employment offer around those risks. A strong appointment should improve readiness between incidents as well as lead an effective response when something goes wrong.
Define the role around business risk
An incident response job description should start with your operating environment. A cloud software company managing customer identities needs different experience from a manufacturer protecting operational technology. Hiring against a generic list of security skills makes it harder to distinguish relevant expertise from an impressive CV.
Before launching the search, document three credible incident scenarios. For each, identify the affected systems, business impact, available internal expertise and decisions that would require executive approval. Include dependencies on cloud providers, outsourced IT teams and critical suppliers.
Translate that exercise into specific hiring outcomes. These might include establishing an escalation process, validating access to investigation data or rehearsing recovery with engineering and operations. Avoid holding the new hire accountable for improvements they cannot authorise or fund.
NIST’s SP 800-61 Revision 3 places incident response within broader cybersecurity risk management. That is a useful hiring principle: preparation and improvement belong in the remit, not just emergency response.
For cyber incident response, the hiring brief should explain what the person must own before, during and after an incident. This is more useful than asking for an arbitrary number of years in cybersecurity.
Choose the coverage model before choosing the candidate
A permanent hire, an external response partner and an outsourced monitoring service solve different problems. Decide how they will work together before publishing the vacancy.
| Model | Most useful when | What the hiring brief must clarify |
|---|---|---|
| Internal response lead | The business needs accountable ownership and coordination | Decision authority, technical remit and access to executives |
| Internal responder or DFIR specialist | Hands-on investigation is the main capability gap | Required platforms, evidence handling and escalation boundaries |
| External incident response retainer | Specialist surge capacity is needed during serious incidents | Activation process, scope, availability and contractual response commitments |
| Managed detection and response service | Monitoring and initial investigation need external support | Where provider responsibility ends and internal incident ownership begins |
DFIR means digital forensics and incident response. An incident commander may have this background, but technical investigation and business-wide coordination are not interchangeable responsibilities.
Similarly, a security operations centre, or SOC, does not automatically provide end-to-end crisis management. Check who will coordinate legal counsel, recovery teams, suppliers and executive communications.
One employee cannot provide sustainable round-the-clock coverage. Cross-Atlantic operations need explicit arrangements for handovers, leave, illness and simultaneous incidents. Time-zone coverage only works if responsibility genuinely transfers between people with the necessary access and authority.
The right cyber incident response model combines clear internal ownership with enough technical capacity and dependable cover. Specify that model first, then recruit the missing capability rather than expecting one appointment to solve every gap.
Give the hire authority that matches the accountability
A job description can promise ownership while the organisation withholds the ability to act. Resolve that contradiction before interviewing.
Agree who can isolate an endpoint, revoke privileged access, interrupt a customer-facing service or activate an external provider. Some actions can be pre-authorised within defined limits. Others need a named executive decision-maker and an alternative if that person is unavailable.
The reporting line also needs explanation. A response lead might report to a CISO or another senior technology leader, but should have a clear escalation route when business continuity and security priorities conflict. Avoid a structure in which they must negotiate access to essential logs during an active investigation.
Legal and compliance responsibilities belong in the brief too. Depending on the organisation, relevant obligations may include GDPR, NIS2, DORA or US sector-specific requirements. These regimes have different scopes and reporting rules. Confirm applicability with legal counsel rather than expecting one hire to interpret every jurisdiction unaided.
For cyber incident response, accountability should include coordinating evidence and escalating notification decisions, not automatically owning the legal determination. HR and legal teams should also confirm on-call arrangements, working-time requirements and any restrictions affecting cross-border access to sensitive data.
Look for evidence of judgement, not just credentials
Certifications can support a shortlist, but they cannot demonstrate how someone handles uncertainty, competing priorities or executive pressure. Assess candidates against the work they will actually perform.
Ask them to describe an incident using anonymised details: the initial signal, their personal contribution, the decisions they made and what changed afterwards. Separate direct responsibility from work performed by colleagues or external specialists.
A credible candidate should explain what was unknown at the time and how that uncertainty affected their choices. Be cautious about accounts in which every incident was resolved flawlessly or the candidate cannot identify a lesson learned.
Relevant technical depth depends on your environment. For a cloud-first business, test understanding of identity compromise, cloud audit logs and SaaS dependencies. For industrial operations, experience with production constraints and safe recovery may matter more than familiarity with common enterprise tools.
Strong cyber incident response candidates should also connect technical actions to business consequences. Listen for clear explanations of containment trade-offs, evidence preservation and recovery criteria, rather than a catalogue of products they have used.
Do not request confidential reports, customer names or sensitive material from previous employers. Anonymised examples and a fictional work sample can provide evidence without rewarding poor professional judgement.
Run a realistic, bounded hiring exercise
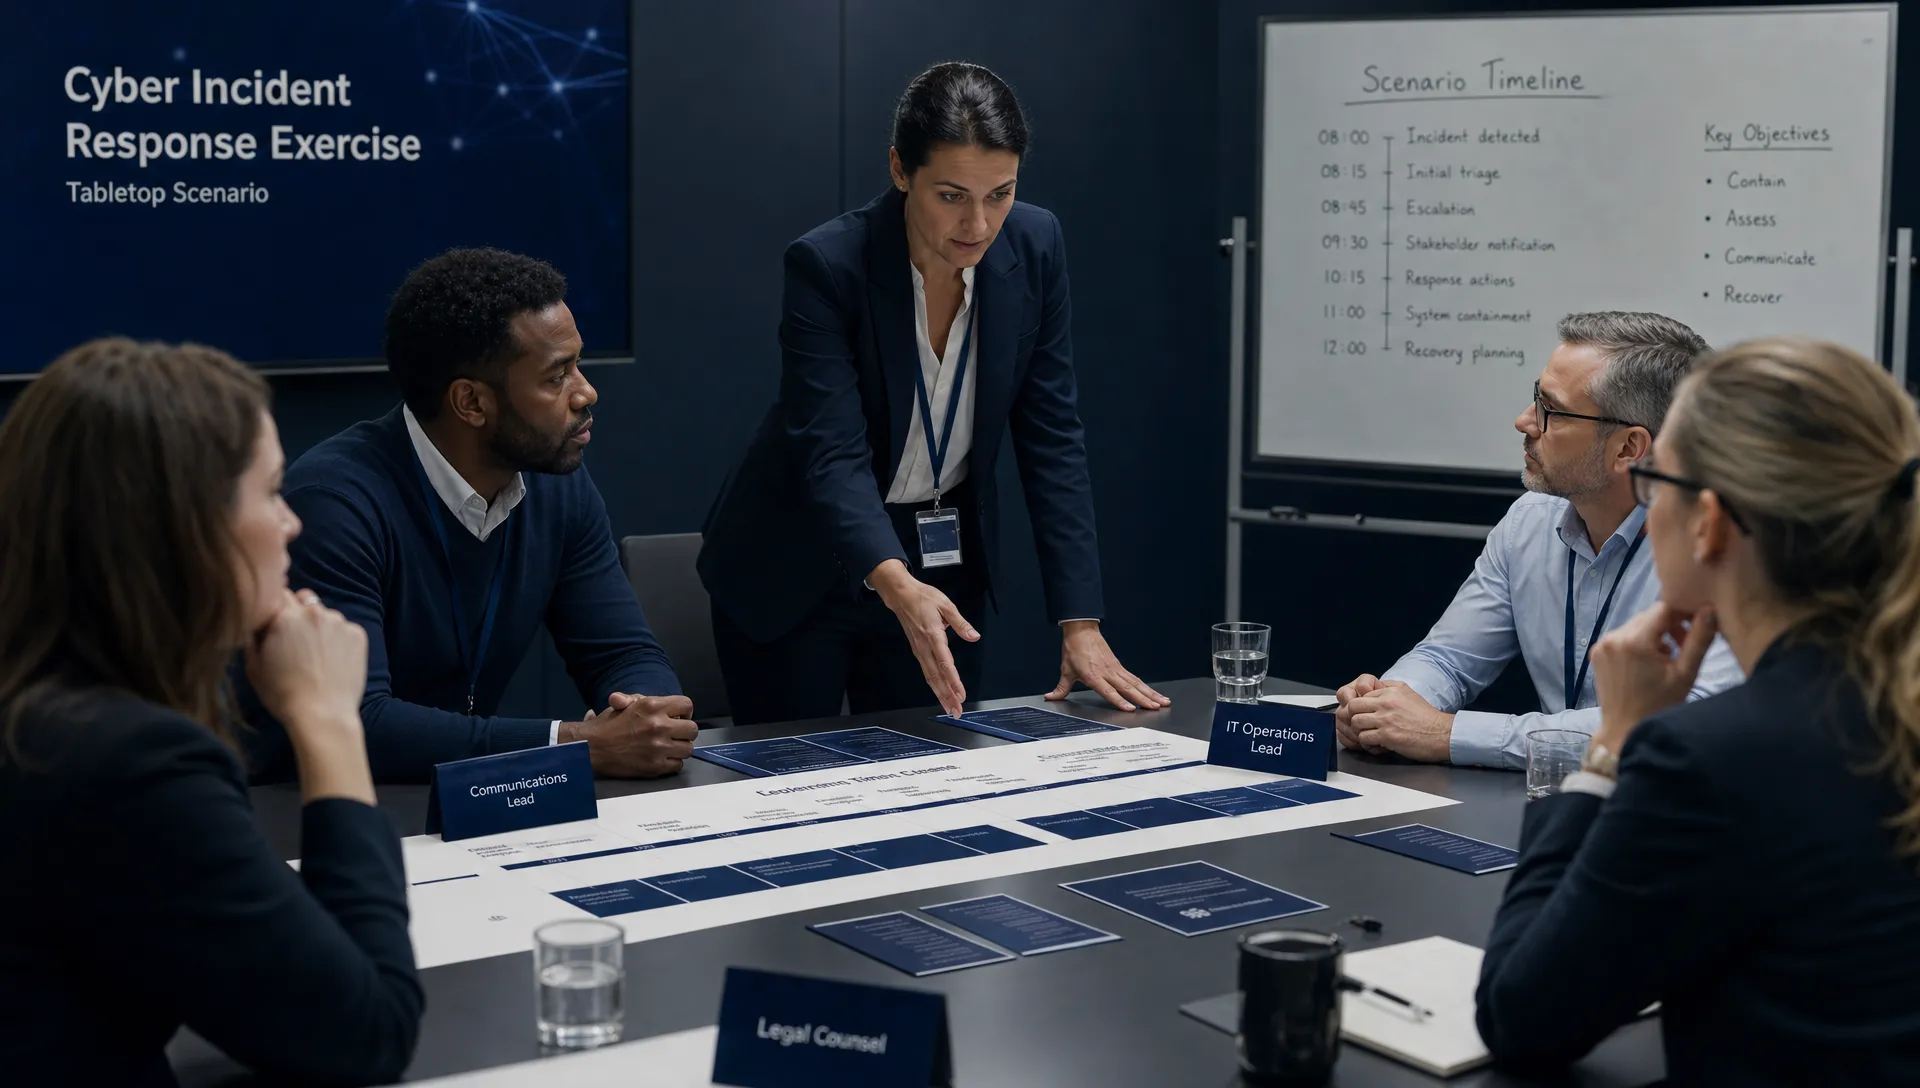
Use a short tabletop exercise alongside structured interviews. Give every candidate the same scenario and assess their reasoning against agreed criteria. A suggested format is a 45 to 60-minute discussion, not an unpaid project that produces operational work for your business.
For example, present a fictional case in which a privileged cloud account shows suspicious activity, a customer-facing service is degrading and the scope of access remains unclear. Include incomplete information so the candidate must identify what they need next.
Ask them to explain their first decisions, who they would involve and which actions require approval. Then introduce a development, such as signs that the compromised identity can access backups. Watch whether they revise their assessment without losing track of the original risks.
Include a brief executive update. The candidate should distinguish confirmed facts from hypotheses, explain business impact and state the next decision required. Precise communication matters more than confident reassurance.
The CISA Tabletop Exercise Packages provide useful references for designing scenarios. Adapt the complexity to the role rather than testing every candidate as though they were a CISO.
A cyber incident response assessment should reward proportionate decisions, useful questions and clear escalation. It should not reward guessing a hidden answer or proposing disruptive containment without considering its consequences.
Use a consistent hiring scorecard
Agree the scoring criteria before meeting candidates. Otherwise, one interviewer may favour technical fluency while another chooses the person who communicates most confidently.
The following weights are illustrative, not a validated industry benchmark. Adjust them to reflect whether you need a hands-on responder or a response leader.
| Assessment area | Illustrative weight | Evidence to seek |
|---|---|---|
| Incident judgement | 25% | Proportionate containment, prioritisation and decisions under uncertainty |
| Technical investigation | 25% | Relevant investigative reasoning and evidence handling |
| Coordination and leadership | 20% | Clear ownership, effective escalation and cross-functional collaboration |
| Executive communication | 15% | Concise updates separating facts, assumptions and decisions |
| Readiness improvement | 15% | Practical lessons, rehearsals and improvements after incidents |
Each interviewer should record evidence independently before the panel discussion. Distinguish a missing skill that can be developed from a fundamental mismatch, such as inability to lead stakeholders when coordination is the role’s primary purpose.
Use references to verify responsibilities and working style, with the candidate’s consent. Ask how they managed pressure, supported colleagues and followed through on improvements. References should corroborate evidence, not substitute for assessment.
Budget for sustainable cyber incident response
An attractive salary will not compensate for a role built around permanent availability and unclear authority. Experienced candidates are likely to examine the operating conditions as closely as the compensation package.
Be transparent about on-call frequency, incident escalation, travel and the balance between hands-on work and leadership. Explain the existing team, external support and approval process for additional resources. If these arrangements are still being developed, say so.
Benchmark pay against the actual role and hiring location rather than a broad cybersecurity title. Incident leadership, specialist forensic work and monitoring roles carry different responsibilities. Where coverage spans Europe and America, employment arrangements and working hours need separate consideration from salary.
The total budget should account for investigation tools, training, exercises, external expertise and cover during absence. A hire without access to these resources may inherit accountability without the means to deliver.
Explain what the candidate will inherit and what they can change. Access to leadership, a realistic improvement budget and protected time for preparation make the offer more credible than a promise to “build everything from scratch” alongside daily operations.
Retention also depends on what happens after a serious incident. Include recovery time, workable cover and constructive reviews, rather than treating exhaustion as evidence of commitment.
Turn the appointment into a 90-day readiness plan
Agree an initial plan before the person joins, then refine it with them once they understand the environment. The aim is to establish usable response capability, not generate documents nobody can execute.
First 30 days: validate access and ownership
The new hire should meet engineering, IT, legal, communications and business continuity stakeholders. Check access to essential investigation data, review external support agreements and verify escalation contacts.
Identify urgent gaps separately from longer-term improvements. Missing administrative access or an untested provider activation process may deserve attention before rewriting a comprehensive policy.
Days 31 to 60: rehearse decisions and handovers
Run a tabletop exercise based on a material business risk. Test who can approve containment, how executives receive updates and how responsibilities transfer outside normal working hours.
For cyber incident response, a useful early measure is whether people can execute their assigned responsibilities with the access and information available. Record delays and unclear decisions, then assign owners to fix them.
Days 61 to 90: test recovery and improvement
Work with system owners to validate recovery procedures and agree the evidence required before restoring affected services. Test selected assumptions safely, using appropriate approvals and change controls.
Report progress through a small set of measures, such as verified escalation contacts, completed recovery checks and resolved exercise findings. Time-to-containment figures can be useful, but only when incident severity and measurement definitions are comparable.
The executive sponsor should remove organisational blockers. A response lead cannot independently fix every dependency across infrastructure, legal and customer operations.
Frequently asked questions
Should we hire an incident response lead or a CISO? Hire against the capability gap. A CISO typically owns broader security strategy, governance and risk management. An incident response lead focuses on readiness and operational response. In a smaller company, responsibilities may overlap, but the workload and supporting resources must make that arrangement viable.
Can an external provider replace an internal hire? External specialists can provide investigation expertise and surge capacity. The business still needs a named internal owner who understands its systems, can secure decisions and coordinates stakeholders. Check the provider’s scope rather than assuming monitoring, containment, recovery and crisis communications are all included.
Which certifications should be mandatory? Make a certification mandatory only where it is genuinely required for the work or a contractual obligation. Relevant credentials can indicate foundational knowledge, but work samples, structured interviews and references provide different evidence. Overly restrictive requirements can exclude capable candidates with equivalent experience.
How should we assess candidates who cannot discuss previous incidents? Respect confidentiality and use anonymised examples or a fictional scenario. For cyber incident response hiring, assess the candidate’s reasoning, personal responsibilities and approach to trade-offs without requesting protected information. A candidate’s refusal to disclose sensitive details can demonstrate sound professional judgement.
Build a hiring brief before opening the search
Before approaching candidates, agree the incidents the role must handle, its decision authority, coverage arrangements and first-quarter outcomes. Add a scorecard and a realistic compensation package. These decisions give recruiters a clearer search mandate and candidates a more credible opportunity.
Optima Search Europe recruits for business-critical and senior executive roles, including within cybersecurity, governance and risk. Discuss the capability your organisation needs, whether that is hands-on response expertise or a leader who can coordinate technical teams and executives. A precise brief helps keep the search focused on the work that matters.

